Let's Encrypt Stopped Emailing Expiry Warnings: How to Get the Alert on Your iPhone
Short version. Let's Encrypt stopped sending expiry emails on June 4, 2025, and since January 15, 2026 it also issues 6-day certificates, so a renewal that fails now has days, not weeks, before the site breaks. Your options: a renewal hook that pushes to your phone, a third-party notification service, or an app that watches the certificate itself. PingKit's Cert Monitor does the last one: one domain free, push to your iPhone at 30, 14, 7 and 1 days and immediately on a chain failure, computed from the newest check you ran. Guardian watches 5 and Guardian Plus 50.
What Changed, and When
For ten years, Let's Encrypt emailed you when a certificate was about to expire. On 22 January 2025 it announced the end of that service, and the last emails went out on 4 June 2025. The reasons it gave were plain: most subscribers now have automated renewal, keeping millions of email addresses tied to issuance records is a privacy cost it would rather not carry, the service cost tens of thousands of dollars a year, and removing it simplifies the infrastructure. It pointed people at third parties instead, naming Red Sift Certificates Lite, which is free for up to 250 certificates.
Then the certificates got shorter. Let's Encrypt issued its first 6-day certificate in February 2025 and made 6-day and IP address certificates generally available on 15 January 2026. They last 160 hours, a little over six days, and you opt in by selecting the "shortlived" profile in your ACME client. The 90-day certificate is still the default, but the direction is clear, and the industry's maximum lifetime is on the same downward path.
Why It Matters More Than It Sounds
Automated renewal fails quietly. The certbot timer gets disabled by a package upgrade. A DNS provider changes its API and the DNS-01 challenge starts failing. A firewall rule blocks port 80 after a "hardening" pass. A wildcard certificate's TXT record stops being writable. None of these produce an error you see; they produce a renewal that does not happen, and the first symptom is a browser warning on a site you thought was fine. With a 90-day certificate, that gap is typically 30 days between the first failed renewal attempt and expiry. With a 6-day certificate, it is a couple of days.
The expiry email used to be the safety net under all of this: a message from outside your automation, saying the thing your automation should have prevented was about to happen. That is what you need to replace: something that is not the renewal job, looking at the certificate the way a browser does.
Option 1: Make Renewal Tell You
certbot runs a deploy hook after every successful renewal. Point it at a push service and you get a notification each time a certificate is renewed:
certbot renew --deploy-hook \
  'curl -s -d "Renewed: $RENEWED_DOMAINS" ntfy.sh/your-private-topic'
ntfy is free and open source; Pushover and similar services work the same way with their own URL. The limitation is in the name: a deploy hook fires on success. A renewal that fails runs no hook, so silence means either "nothing needed renewing" or "renewal is broken", and you cannot tell which without a second job that checks the certificate's actual expiry. That second job is what the next two options are.
Option 2: A Notification Service
Red Sift Certificates Lite is the one Let's Encrypt recommends and is free up to 250 certificates. UptimeRobot includes certificate expiry alerts on its paid plans from $9 a month. Both watch the certificate from the outside and email you, which restores the old safety net exactly, with the old delivery channel: an email, in an inbox, that you may or may not read in time.
Option 3: Watch the Certificate From Your Phone
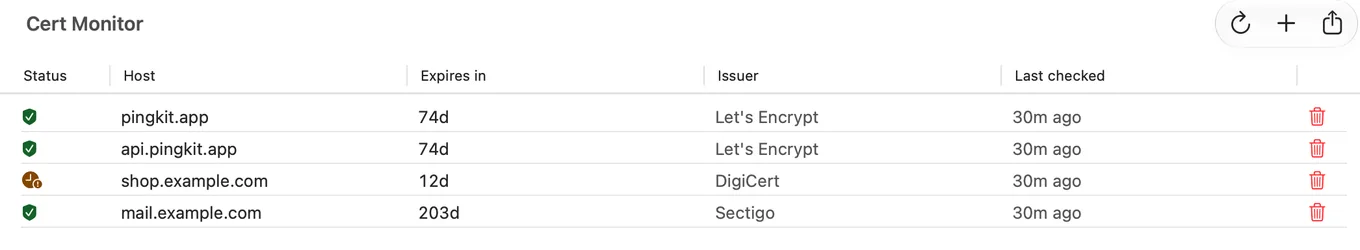
PingKit's Cert Monitor does the same outside check and delivers it as a push notification. Add a domain, and a port if it is not 443. On the iPhone a check runs when you tap Poll all now; in the Mac Agent every domain is polled once an hour for as long as the Agent is running. Each check connects over TLS, reads the chain and reports to PingKit's backend, which pushes to your iPhone 30, 14, 7 and 1 days before expiry and immediately if the chain stops validating: a missing intermediate, a name mismatch, an untrusted root. The push is computed from the newest report, and a report over three hours old does not count, so an old reading never raises a warning. The Mac cannot receive a push; with Guardian the Agent shows its own notification at the same thresholds for the domains in its list, and Guardian Plus can send every alert by email too, which is the old delivery channel back if you want it, or to a webhook.
One domain is free, permanently, with the full schedule. Guardian raises the limit to 5 for $2.99 a month or $24.99 a year. Guardian Plus raises it to 50, adds a signed compliance PDF and can send the alerts by email or to a webhook; it is $4.99 a month or $39.99 a year in the Mac Agent, $9.99 a month or $79.99 a year on iPhone and iPad. Every plan has a 1-week trial.
Setting It Up
- Install PingKit on your iPhone. That is where the expiry push lands, because macOS has no push channel for this. The free PingKit Agent on a Mac that stays on gives you the same inventory and polls it hourly for as long as the Agent is running; with Guardian it shows its own notification on the Mac, and with Guardian Plus its alerts can go by email.
- Open Cert Monitor (the Monitor tab on iPhone; the Cert Monitor pane on Mac), add the domain, and allow notifications when asked.
- The first check runs immediately and shows the issuer, expiry and days remaining. If the domain is behind a load balancer with several certificates, add it once; the check reads whichever certificate the connection is served.
- Keep the deploy hook from Option 1 as well. A renewal push plus an expiry push covers both halves: you hear when renewal works, and you hear when it has not.
With 6-Day Certificates
The 30, 14 and 7 day thresholds never fire for a certificate that lives six days; the one that matters is the 1-day alert, and on a 6-day certificate it fires only if automated renewal has already failed, because a working renewal replaces the certificate long before then. The chain-failure alert applies as always. If you have opted into the shortlived profile, treat the 1-day push as an alarm, not a reminder.
Honest Limits
- The iPhone does not check in the background; iOS does not allow it. A check on the phone is a tap, and the expiry push is computed from your newest check, so treat this as a watch list you check into. For coverage that runs without you, use a service in Option 2 alongside it.
- Cert Monitor reports what the connection is served. It does not read your ACME logs and cannot tell you why a renewal failed, only that the certificate is running out.
- It does not report the negotiated TLS version or cipher suite.
- More than one domain needs Guardian (up to 5) or Guardian Plus (up to 50). The free tier is one domain, not one certificate per domain.
Frequently Asked Questions
When did Let's Encrypt stop sending expiration emails?
The service ended on June 4, 2025, announced on January 22, 2025. Let's Encrypt cited widespread automated renewal, the privacy cost of retaining millions of email addresses, a cost of tens of thousands of dollars a year, and infrastructure simplification, and recommended third-party services such as Red Sift Certificates Lite instead.
How do I get notified before my Let's Encrypt certificate expires?
Watch the certificate from outside your renewal job. PingKit's Cert Monitor does this with a push to your iPhone at 30, 14, 7 and 1 days before expiry and immediately on a chain failure; one domain is free. A certbot deploy hook that pushes on successful renewal is a good complement, but it cannot tell you when renewal fails.
Does Let's Encrypt issue 6-day certificates now?
Yes. Six-day and IP address certificates became generally available on January 15, 2026. They last 160 hours and you opt in with the shortlived profile in your ACME client. The 90-day certificate remains the default.
Is there a free SSL expiry monitor for iPhone?
PingKit's Cert Monitor watches one domain free, permanently, with push notifications. Guardian raises the limit to 5 domains for $2.99 a month, and Guardian Plus to 50: $4.99 a month on Mac, $9.99 a month on iPhone and iPad.
Why not just rely on certbot's renewal?
Because renewal fails silently. A disabled timer, a broken DNS challenge or a firewall change produces no error you see, only a renewal that does not happen. An outside check of the certificate's real expiry is the only thing that catches that, and it used to be the email.
Watch one domain free, with the push on your iPhone.
Free to download. One domain is free with push. Guardian Plus is $9.99 a month or $79.99 a year on iPhone and iPad, $4.99 a month or $39.99 a year on Mac. Every plan has a 1-week trial.
Download PingKit for iPhone